ARP Spoofing Explained: How Man-in-the-Middle Attacks Work
Learn how ARP spoofing and man-in-the-middle attacks work, and see what a good cyber security course in Kolkata should teach you to build real skills.
If you are planning a cyber security course, ARP spoofing is one of the first attacks you will practise in the lab. It looks simple, yet it shows how a whole network can be fooled with a few fake messages. This guide explains how ARP spoofing works, how it leads to man-in-the-middle attacks, how to spot it, and what to look for in cyber security training.
What Is ARP Spoofing?
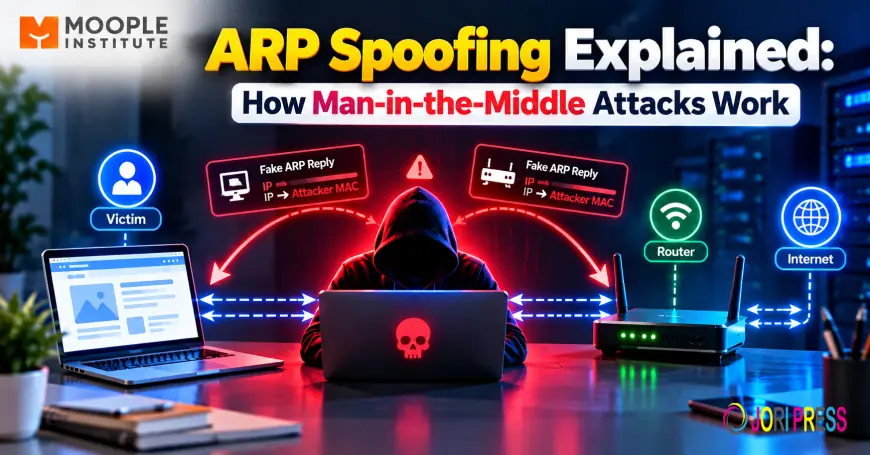
ARP spoofing is an attack where a hacker sends fake Address Resolution Protocol messages on a local network to link their own MAC address with another device's IP address. This lets the attacker secretly intercept, read, or change data moving between two devices, which is known as a man-in-the-middle (MITM) attack.
Why ARP Is Easy to Trick
ARP helps devices find each other. When your laptop wants to reach the router, it asks, "Who has this IP address?" The router replies with its MAC address. The problem is that ARP has no built-in way to check who is answering. Any device on the network can reply, and most devices simply believe it.
How a Man-in-the-Middle Attack Works
Here is the usual sequence in an ARP-based MITM attack:
-
The attacker joins the same local network (for example, public Wi-Fi).
-
They send fake ARP replies to the victim, claiming to be the router.
-
They send fake replies to the router, claiming to be the victim.
-
Both devices update their ARP tables with the wrong information.
-
All traffic now passes through the attacker's machine.
What Can the Attacker Do?
-
Read unencrypted data such as old HTTP pages or chat messages
-
Capture login details on insecure sites
-
Redirect users to fake pages
-
Drop or change data in transit
Expert tip: HTTPS protects most of your content, but it does not stop ARP spoofing. It only limits what the attacker can read.
A Real-Life Example
Imagine a student working from a busy café in Kolkata. An attacker on the same Wi-Fi runs a spoofing tool. The student's laptop now sends every request to the attacker first, and the page still loads normally, so nothing looks wrong. This is why ARP spoofing is dangerous: it is quiet. In a good lab, students recreate this safely on their own virtual machines to see it happen.
ARP Spoofing vs Other Network Attacks
|
Attack |
Where It Happens |
Main Goal |
Typical Defence |
|
ARP Spoofing |
Local network (Layer 2) |
Intercept traffic |
Dynamic ARP Inspection, static entries |
|
DNS Spoofing |
DNS responses |
Redirect to fake sites |
DNSSEC, secure DNS |
|
Session Hijacking |
Active user sessions |
Take over accounts |
HTTPS, secure cookies, short sessions |
How to Detect and Prevent ARP Spoofing
Warning Signs to Watch For
-
Two IP addresses sharing the same MAC address in your ARP table
-
Sudden slow internet on a local network
-
Unexpected browser certificate warnings
How to Prevent It
-
Enable Dynamic ARP Inspection on managed switches
-
Use static ARP entries for critical devices
-
Avoid public Wi-Fi for sensitive work, or use a trusted VPN
-
Use monitoring tools such as Wireshark or arpwatch
For deeper guidance, the CISA guidance on securing networks and NIST's cybersecurity resources are trusted starting points.
Common Mistakes Beginners Make
-
Practising on real networks instead of an isolated lab (this can be illegal)
-
Skipping the basics of TCP/IP and the OSI model
-
Learning tools without understanding why they work
-
Assuming HTTPS makes every attack harmless
What to Look for in a Cyber Security Course
Attacks like ARP spoofing are only useful to learn if you practise them ethically. At Moople Institute, our focus is on practical, project-based learning, and any strong cyber security course should follow the same idea. Look for these features:
-
Hands-on labs: virtual machines, Wireshark, Kali Linux
-
Clear syllabus: networking, ethical hacking, web security, incident response
-
Certificate: a recognised cyber security course certificate, plus guidance for exams like CEH or Security+
-
Transparent cyber security course fees: with clear instalment options
-
Mentors with industry experience
Some students choose a BSc in cyber security at a university, which takes three years. A focused training institute course is a faster route to job-ready skills, and many students combine both. When comparing the best cyber security colleges in Kolkata, ask to see lab sessions, sample projects and placement support first.
FAQs
1. What is ARP spoofing in simple words?
It is when an attacker lies to devices on a network about who owns an IP address, so traffic flows through the attacker.
2. Is ARP spoofing the same as a man-in-the-middle attack?
No. ARP spoofing is one method used to carry out a man-in-the-middle attack.
3. Can HTTPS stop ARP spoofing?
No, but it encrypts data so the attacker cannot easily read it.
4. Is it legal to practise ARP spoofing?
Only on networks you own or have written permission to test, such as a training lab.
5. Which cyber security training institute in Kolkata is right for me?
Choose one with live labs, an updated syllabus, experienced trainers and clear fees.
Conclusion
ARP spoofing shows why network basics matter in security. If you want to learn these skills step by step, explore our cyber security training options and compare the syllabus, certificate and fees. Start with networking fundamentals, practise only in safe labs, and build a small portfolio of documented attack-and-defence projects.
Ready to start? Book a free counselling session at Moople Institute to see the course syllabus, lab setup and fee details for your batch.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0