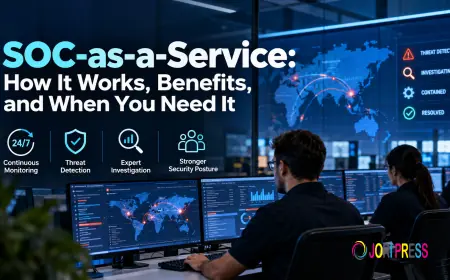

SOC-as-a-Service: How It Works, Benefits, and When You Need It
Learn how SOC-as-a-Service works, its key benefits, and how 24/7 security monitoring helps businesses detect, investigate, and respond to threats.
Cyber threats do no longer observe enterprise hours. A suspicious login in the dead of night, an uncommon file down load over the weekend, or sudden pastime in a cloud utility ought to all suggest a security issue that wishes research.
For groups with restrained cybersecurity resources, monitoring those sports around the clock can be difficult. Security tools generate alerts, however a person nevertheless needs to study them, decide which ones rely, and determine what action to take.
SOC-as-a-Service (SOCaaS) addresses this assignment with the aid of imparting continuous security tracking, chance detection, and expert investigation thru an outside safety operations middle.
This article explains what SOC-as-a-Service is, the way it works, its benefits, and what groups need to bear in mind before choosing a company.
What Is SOC-as-a-Service?
SOC-as-a-Service is a managed cybersecurity solution that lets businesses use a security operations center without having to create one themselves.
A SOC is a team of security experts who watch systems look into behavior check security alerts and help with responding to incidents.
Through SOC-, as-a-Service a third-party company provides these services using security tools, skilled analysts and proven monitoring routines.
Depending on the service scope, a managed SOC can monitor security activity across:
-
Business networks and servers
-
Employee computers and endpoints
-
Cloud applications and infrastructure
-
Identity and authentication systems
-
Firewalls and other security tools
The goal is to identify potentially harmful activity, investigate alerts, and provide the information needed to respond before threats cause further damage.
How Does SOC-as-a-Service Work?
SOC-as-a-Service integrates the collection of security information, threat detection capabilities, and human evaluation skills to detect suspicious activities within the company’s IT infrastructure.
Even though the process varies among different vendors, SOC-as-a-Service generally entails the following steps.
1. Security Data Collection
The process begins by collecting security logs and events from connected systems.
A security log is a record of activity occurring within a device, application, or network. For example, a log might record a failed login attempt, an administrator changing account permissions, or a security tool detecting suspicious software.
These records provide the information analysts need to understand what is happening across the environment.
2. Centralized Monitoring and Correlation
Collected security data is analyzed through a Security Information and Event Management (SIEM) platform.
A SIEM brings security events from multiple sources together and applies detection rules and analytics to identify suspicious behavior.
For example, several failed login attempts followed by successful access from an unfamiliar location could trigger an alert.
Looking at related events together can reveal activity that might be missed when security tools operate independently.
3. Threat Detection and Alert Generation
Detection technology examines incoming events for indicators of potentially malicious activity.
These indicators may include unusual account access, suspicious network communications, unauthorized configuration changes, or behavior associated with known attack techniques.
When activity matches a detection rule or risk pattern, the system generates an alert for review.
However, an alert does not necessarily mean an attack has occurred. Legitimate business activities can sometimes trigger security warnings.
4. Alert Triage and Investigation
Security analysts review generated alerts to determine their relevance and severity.
This process is called alert triage.
Analysts examine available evidence, compare related events, and investigate whether the activity represents a genuine security threat or a false positive.
For example, an employee signing in from a new location could be legitimate travel or a sign of compromised credentials.
The analyst uses available context to assess the situation rather than treating every unusual event as a confirmed attack.
5. Incident Escalation and Response Support
When analysts identify a potential security incident, they escalate their findings according to the agreed procedures.
Depending on the provider's responsibilities, this may involve notifying the internal IT team, recommending corrective actions, or initiating authorized response procedures.
Possible actions include reviewing affected accounts, investigating suspicious endpoints, restricting access, or coordinating further investigation.
The specific response activities included in a SOC-as-a-Service contract should be clearly defined.
6. Security Reporting and Continuous Improvement
SOC services also provide reporting to help businesses understand security activity over time.
Reports may summarize investigated alerts, security incidents, detection trends, and recommended improvements.
This information helps organizations review recurring problems, assess their monitoring coverage, and identify areas requiring additional security controls.
Key Benefits of SOC-as-a-Service for Businesses
1. Continuous Security Monitoring
Lots of organisations have IT teams that are essentially working only during normal business hours.
However, the suspicious activity can happen overnight, on the weekend or during the holidays.
SOC-as-a-Service provides continuous monitoring so that security alerts can be reviewed outside of normal operating hours.
This helps to reduce the lag between an anomaly being spotted and an analyst commencing an investigation.
2. Access to Experienced Security Analysts
Investigating cyber threats requires a certain amount of specialist knowledge and experience.
Organisations need people who understand the attack techniques, the security logs, the detection systems and the incident investigation.
Hiring and keeping analysts with these skills is a real challenge, especially for smaller IT teams.
An outsourced SOC gives you access to security professionals without the need for your business to go out and recruit and manage a full monitoring team in-house.
3. Reduced Operational Burden on IT Teams
Internal IT will of course be responsible for employee support, system maintenance, software updates, access requests and infrastructure changes.
Looking at vast numbers of security alerts is another job on top of the rest.
With a managed SOC the external analysts will be responsible for monitoring the alerts and initial investigation within the agreed service scope.
This enables the internal teams to focus on the IT ops and security issues that they need to be involved in.
4. Increased Visibility Throughout the Security Infrastructure
Most businesses use multiple security products, which all create their own set of alerts and activity logs.
There is a risk that without oversight from one centralized place it's challenging to piece together what is happening across all of the sources.
SOC-as-a-Service assists in presenting the appropriate security data in one place to be viewed and actioned.
For instance, if we see abnormal activities coming from an employee account, the signals may show up in identity logs, endpoint alerts, and cloud application logs.
Putting those things together gives more perspective for understanding the risk.
5. More Consistent Threat Investigation
Different security alerts demand different responses.
Some alerts are not false positives but require further investigation.
A managed SOC would follow pre-designed processes to analyze the alerts, determine severity and escalate the alerts that are important.
This allows businesses to handle security events more uniformly, instead of completely dependent on employees' availability or discretion.
6. Predictable Security Monitoring Expenses
Running an internal SOC requires investment in security solutions, staff, training, processes, and maintenance.
SOC-as-a-Service generally uses a recurring subscription model.
This makes the tracking costs easier to plan for, though the prices are related to the monitored assets, amounts of data, coverage needs, and offered services.
Services should be compared on the basis of total value offered by a service and cost involved not the subscription prices.
SOC-as-a-Service vs. In-House SOC: What's the Difference?
Both models aim to identify and investigate security threats. The main differences involve operational responsibility, staffing, infrastructure, and control.
| Factor | In-House SOC | SOC-as-a-Service |
|---|---|---|
| Security analysts | Recruited and managed internally | Provided by an external provider |
| Monitoring coverage | Depends on internal staffing | Based on contracted coverage |
| Security tools | Typically managed internally | Provider-managed or jointly managed |
| Initial investment | Often higher due to staffing and infrastructure | Typically subscription-based |
| Operational control | Greater direct control | Shared responsibilities defined by contract |
| Scaling | May require additional hiring and infrastructure | Depends on provider capacity and service agreement |
| Maintenance | Primarily internal responsibility | Shared or provider-managed |
An in-house SOC can be suitable for corporations that need big customization, direct operational control, and committed inner security assets.
SOC-as-a-Service can be suitable for companies that want ongoing monitoring but do no longer need to build a complete security operations middle.
Some organizations additionally adopt a hybrid model, wherein an outside SOC supports an existing inner protection crew.
SOC-as-a-Service vs. SIEM: Are They the Same?
SOC-as-a-Service and SIEM are connected,. They have different roles.
SIEM is a technology platform. SOC-as-a-Service is a managed security operation that uses technology and security analysts.
A SIEM collects, analyzes and connects security event data to help find threats.
A SOC goes beyond that by having analysts look at alerts check activity figure out the risk and handle the steps to respond.
For example a SIEM might notice that an administrator account logged in from a place.
The SOC analyst then looks at actions decides if the event is a problem and takes the right actions as agreed in the service contract.
What Types of Cyber Threats Can SOC-as-a-Service Help Detect?
The types of threats that a managed SOC will be able to detect will vary based on the types of security technology, log sources, and integrations used by the managed SOC services provider.
Examples of common types of threats that a managed SOC will be able to detect include:
Suspected Unauthorized Login Attempts
Repeated failed login attempts, strange sign-in activity, and other forms of account activity can mean that there are attempts to compromise your organization.
Compromised User Credentials
Strange changes in account activity, permissions, and access could point to the fact that your credentials have been compromised.
Malware
Security events from the endpoint security solutions or network monitoring solutions used by the managed SOC provider can be used to detect signs of malware.
System Changes
Unexpected changes in your system configuration, security settings, and privileges may need investigation.
Suspicious Network Activity
Connections to malicious IP addresses and other forms of unexpected network activity could indicate potential security incidents.
Lateral Movements
After gaining access to one system, attackers often attempt to move laterally and gain control over other systems.
This can be detected via correlation of identity, endpoint, and network activity. Detection is not guaranteed for all possible threats.
A SIEM, by itself does not take the place of the people and the steps needed to look into security issues.
When Should a Business Consider SOC-as-a-Service?
SOC-as-a-Service may be a good fit when an organization is experiencing any of the conditions listed below.
No Security Monitoring After Business Hours
With alarms only being checked during employee availability, critical events can go unnoticed for years.
This is where continuous SOC monitoring comes in to bridge the gap.
The IT Team Receives Too Many Security Alerts
Security tools may produce too many alerts for a single team to effectively handle.
A managed SOC can triage and review alerts so the business can focus on findings that require action.
The Business Has a Variety of Cloud and Security Platforms
The more apps, devices, and services an organization integrates, the more complex it becomes to monitor security events from different systems.
Greater visibility in support environments. Centralized security monitoring.
Bringing on a Dedicated Security Team Doesn't Make Sense
An internal SOC may be too resource-intensive for a business to operate, whether due to budget or employee constraints.
Another option to find advanced protection is through an outsourced service.
Organization Must Improve Its Reporting of Security
There could be requirement for evidence of incidents investigated, security monitoring and controls in an organization.
SOC reporting but the use of a SOC does not natively create regulatory requirements.
What to Look for in a SOC-as-a-Service Provider
Choosing a SOC company involves extra than evaluating month-to-month pricing.
Businesses have to compare the issuer's technical abilties, carrier commitments, operational approaches, and responsibilities.
Monitoring insurance: Confirm which devices, applications, cloud environments, and security gear can be monitored.
Security generation: Understand which SIEM, analytics, and detection technology the provider makes use of.
Analyst availability: Verify whether or not analysts provide non-stop monitoring and what assist is to be had out of doors normal commercial enterprise hours.
Incident escalation: Review how security incidents are prioritized, suggested, and escalated to the inner crew.
Response obligations: Determine whether the company investigates and recommends actions or can also carry out permitted containment and remediation sports.
Service-degree agreements: Review commitments for alert dealing with, escalation, and verbal exchange, including the conditions below which each SLA applies.
Reporting: Ask what data seems in security reports and how often reviews are added.
Pricing and contract phrases: Check onboarding fees, tracking limits, facts retention, extra carrier fees, and contract flexibility.
These concerns assist groups evaluate companies based on their actual protection wishes.
How SafeAeon SOC-as-a-Service Supports Security Operations
SafeAeon offers SOC-as-a-service for those organizations which require continuous security monitoring and investigations without creating their own SOC.
The service includes security technologies with skilled analysts who will analyze suspicious activity, investigate alerts, and communicate security findings to customer teams.
Capabilities offered by this service are:
- 24/7 security monitoring: Ongoing monitoring of supported systems and security events.
- Centralized security analysis: SIEM-based security logs collection and correlation to detect suspicious activities.
- Alerts triage by analysts: Investigation of alerts to determine if security incidents happen or it is just a false positive.
- Incidents escalation: Security findings, incidents details, and next steps communication.
- Threat intelligence: Threats information to perform better security analysis.
- Security reports: Reports which allow businesses to analyze activities and find trends in security operations.
- Subscription-based service delivery: Subscription-based delivery which helps to minimize requirements for internal fully-staffed SOC.
Also, SafeAeon SOC-as-a-Service page describes SOC 2 Type II and ISO 27001 certifications, month-to-month subscriptions, and 30 minutes Gold SLA. Applicability of specific service commitments should be clarified based on the chosen plan and agreement.
Thus, organizations may analyze SafeAeon SOC-as-a-Service to learn about offered service capabilities.
Conclusion
SOC-as-a-Service gives businesses access to continuous security monitoring and professional threat investigation without requiring them to operate a complete in-house security operations center.
By bringing together security data, detection technology, and trained analysts, the service helps organizations identify suspicious activity, investigate alerts, and make better-informed incident response decisions.
For businesses with limited internal security resources, an outsourced SOC can provide additional monitoring capacity while allowing existing IT teams to focus on their operational responsibilities.
Looking for 24×7 security monitoring?
Explore SafeAeon's SOC-as-a-Service or schedule a consultation to discuss your security monitoring requirements.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0